Passwords prove nothing.
Phished, shared and never tied to a person.
Home / Platforms
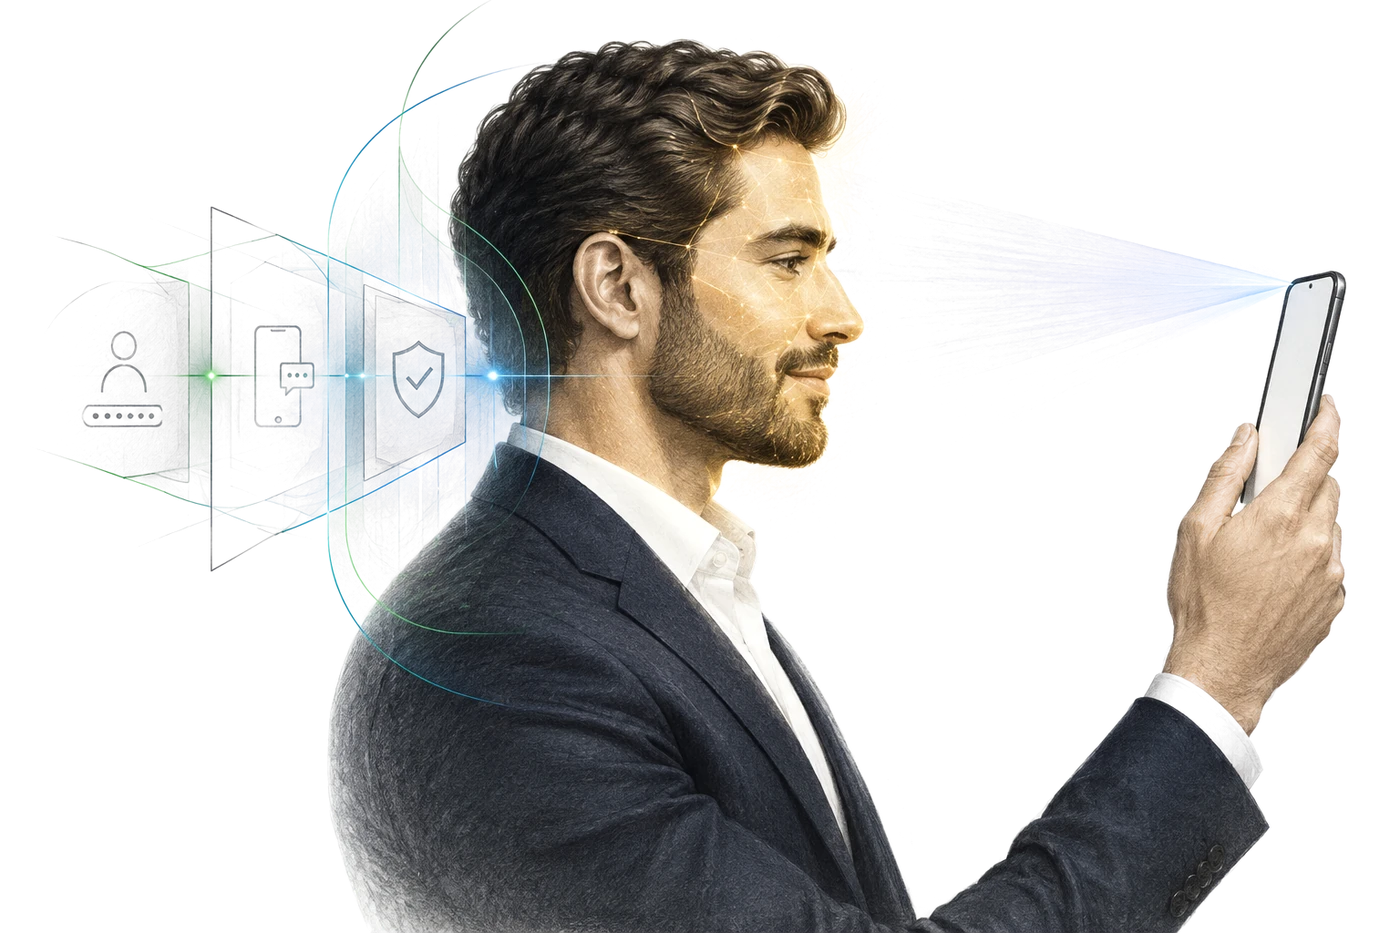
Multi-factor authentication with genuine identity assurance, where no biometric data is ever stored, transmitted, or exposed. Anywhere. Privacy-preserving biometrics, built with dynamic linking and MFA by design. Available on-premises and as SaaS.
Secure identity. Simplified.
Digital services without passwords, usernames, SMS OTPs or external MFA tools. Every element is bound together cryptographically, so trust is proven, never assumed.
Standards
Today's security challenges
Phished, shared and never tied to a person.
It cannot show who is actually using it.
Impersonation needs no access at all.
Exposed to deepfakes, siloed, and stored as a honeypot.
They unlock the device, not the identity, and fall back to a PIN.
They rely on device biometrics, so a PIN can stand in for the person.
No dynamic link to what the user approves.
No binding proof of who authorized each transaction.
None of these methods can prove that the person authenticating is the same person who enrolled.
The security paradox
Server-side biometric storage creates honeypots. Device-native biometrics authenticate the device, not the person: under NIST guidance a biometric is not an authenticator on its own, only an activation factor that unlocks the device's key.* The bank never learns whose face unlocked it, or whether a PIN did.
Privacy-preserving biometrics resolve the paradox: no complete template is ever created, stored or transmitted. Not on the device, not on the server, not anywhere in between.
* NIST SP 800-63B implementation resources. pages.nist.gov
How it works
Each factor is verified independently. True MFA, not layered security.
Privacy-enhancing facial recognition with anti-spoofing liveness detection. Biometric data is transformed with secure multi-party computation before it leaves the device, and is never stored.
Cryptographic device binding, verified independently of the biometric. A PIN cannot stand in for the person.
Customer authentication
Keys in the device's secure hardware make authentication inseparable from a verified device.
One biometric action replaces passwords and SMS OTPs, authenticating the user and the device.
Strong customer authentication tied to the exact amount and payee.
Higher assurance for high-value or privileged actions, with a seamless biometric challenge.
Self-service recovery using true biometric identity. No helpdesk, no SMS codes.
A biometric scan certified by global standards, or enrollment from your existing KYC.
The regulatory shift
The burden of proof has moved to the bank. A bank that cannot prove who approved a payment will pay for it.
When a customer disputes a payment, the bank must prove it was authenticated, and use of a credential is not, on its own, proof of authorization.1
Victims of authorised push payment fraud must be reimbursed since October 2024.2
Agreed payment reforms make banks refund impersonation fraud and cover losses where fraud controls fall short.3
Singapore assigns phishing losses to banks and telcos that miss their duties.4
Regulatory alignment
Value delivered
No passwords, PINs or OTPs to phish.
One glance replaces multi-step flows.
Self-service recovery, no helpdesk.
iOS, Android and web: any device with a camera.
FIDO2-certified and built on open standards.
Designed to support PSD2, GDPR and eIDAS requirements.
The same capabilities, standards and security model in both.
Installed in your own data centre. Customer data, server-side keys and audit records stay within your environment and your governance.
Fully managed and ready to integrate, for organizations that want to start quickly without running infrastructure.
Let's discuss how Imagineers can strengthen your organization's security posture and identity infrastructure.
Ibn Zuriek St., Jubaiha
Amman, Jordan
Sunday to Thursday, 9:00 AM – 5:00 PM (GMT+3)